Build and deploy your applications with builds, registries and PR previews, on infrastructure you control.
Self-hosted. Free community edition. Yours.
helm install kaisin oci://ghcr.io/bluepawlabs/charts/kaisin
Your infrastructure.
Your data.
Your rules.
This is the real reason people rent. Not the servers. The forty files.
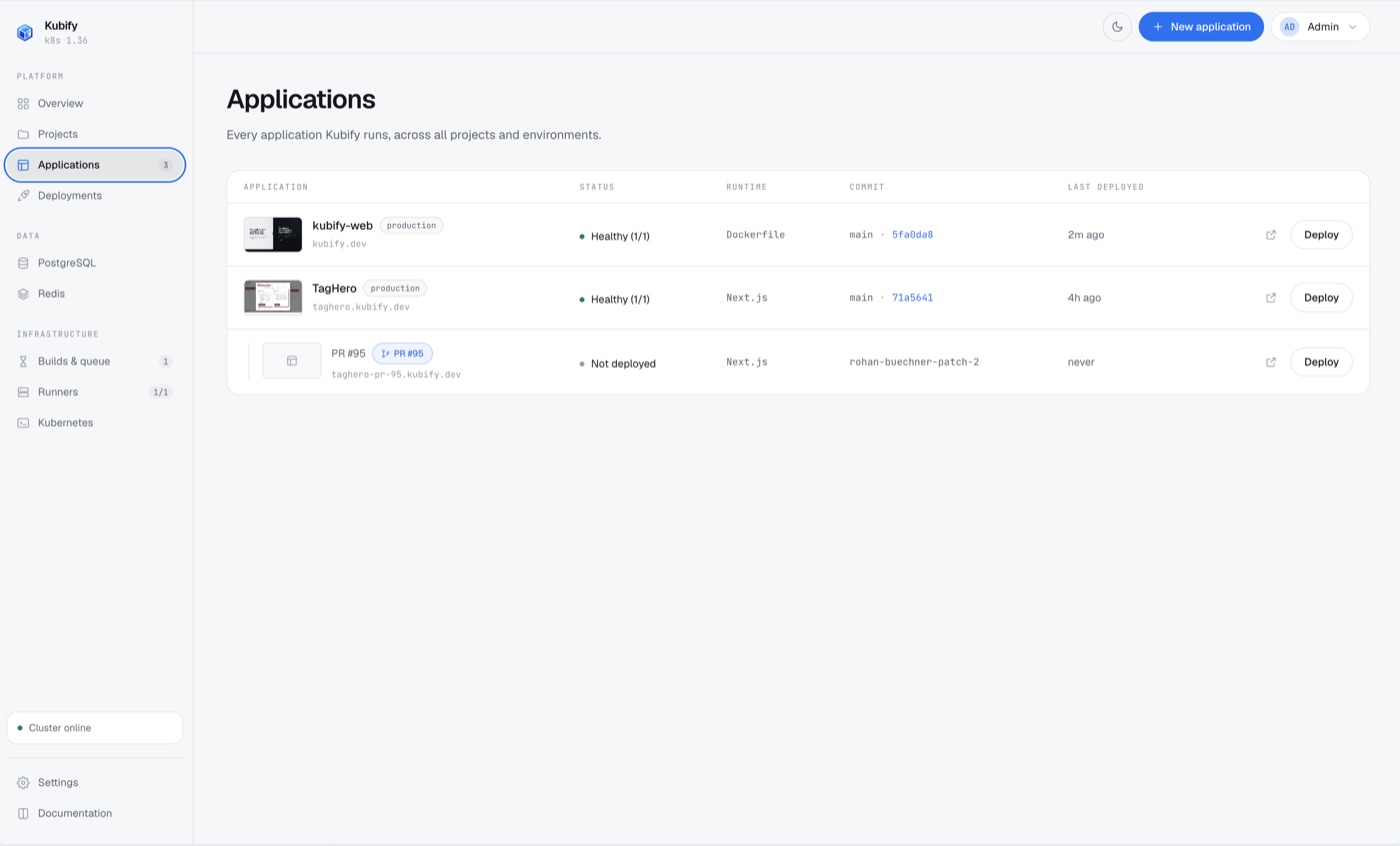
It installs into a cluster you already have. Connect a repo, and Kaisin builds on your nodes, pushes to a registry it runs, rolls the image out, gets TLS from cert-manager, and gives every pull request its own environment that disappears when the PR closes.
Deployment, Service and Secret you can read with kubectl and delete without asking anyone.
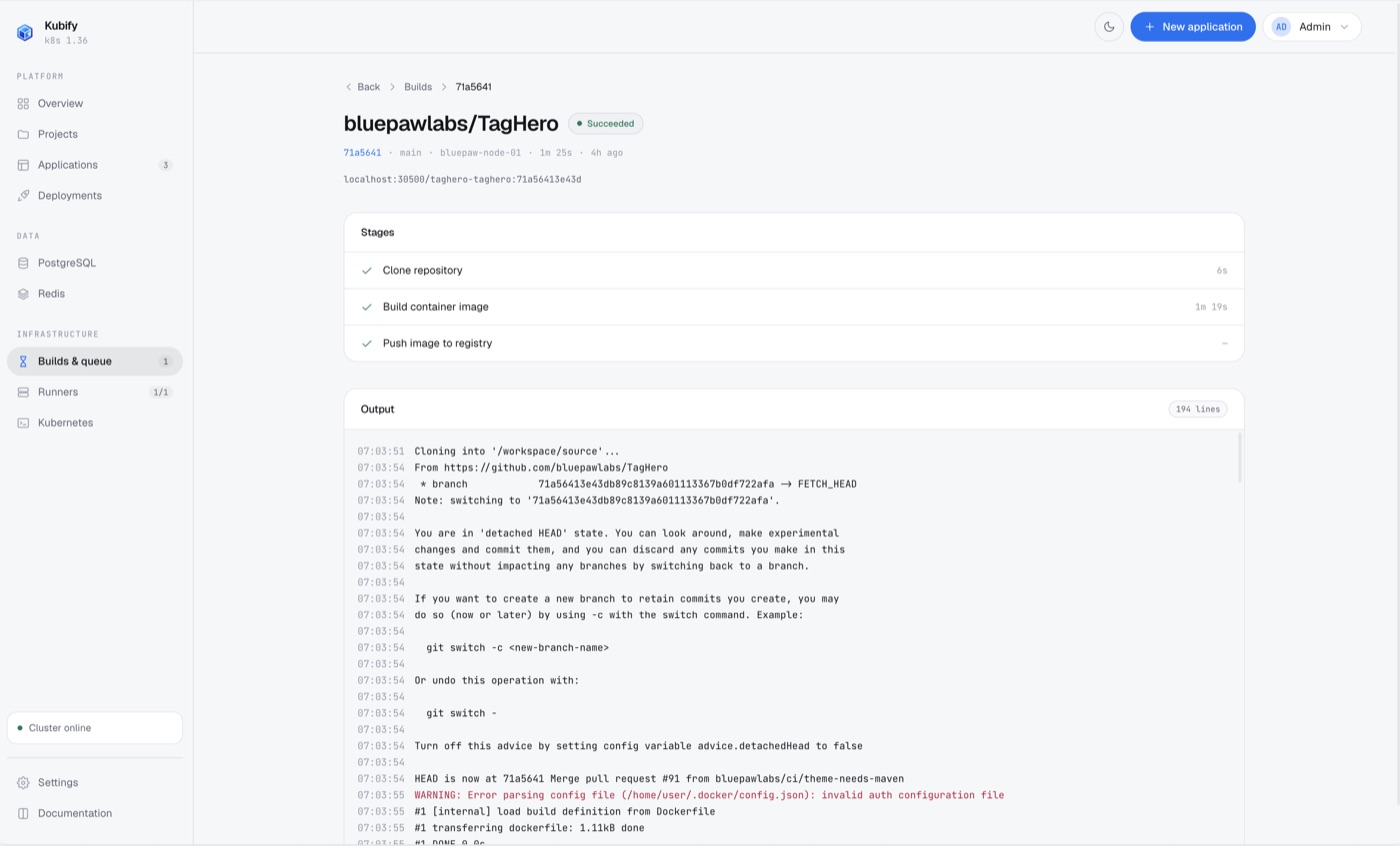
Rootless BuildKit in a short-lived Job. No Docker socket, no privileged pod.
An in-cluster registry on a volume you own. Keeps the last ten images per app.
A route and a certificate per hostname, issued automatically once DNS points here.
PostgreSQL and Redis per environment, with the connection string injected as a Secret.
A namespace, a build of the exact commit, and a hostname per PR. Removed when it closes.
Standard Kubernetes objects, top to bottom. No opaque controller to debug at 2 AM.
Because Kaisin creates standard Kubernetes Secrets, you can inject external connection strings exactly like you do today. Point production at your existing RDS or managed Postgres; use the in-cluster databases for PR branches.
external managed DB support: confirm exact scope in the docs
From pull request opened to preview running. Measured on the reference installation: a Next.js app on a single node.
You are pasting a cluster-level chart, so inspect it first. Pull it, template it, and read every object it would create. Nothing reaches your nodes that you have not already seen.
View on GitHubEverything Kaisin makes is an ordinary Deployment, Service and Secret that you can read with kubectl and delete without asking anyone.
No account to create and nothing to buy to run it. Telemetry goes to your own collector, or nowhere at all.
Native to k3s, kind, and any existing Kubernetes cluster. Uses cert-manager for TLS, rootless BuildKit for builds, and the OCI registry at oci://ghcr.io/bluepawlabs/charts/kaisin. Where Coolify and Dokploy target raw Docker servers, Kaisin is built for the cluster you run.
Pick your machine and your cluster. Copy the command.
The community edition, free. No account, nothing to sign.
Encryption key: Kaisin makes its own encryption key. Back it up. Losing it makes the secrets it protects unrecoverable.
Deleting Kaisin leaves your running apps, services and certificates intact, because they're standard Kubernetes objects. You can rip it out the same way you rip out anything else.
Free community edition. No account to create.
 Kaisin